Showing posts with label X-Ways Forensics. Show all posts

Tuesday, June 20, 2017

Virtualization of a raw image of an Apple OS X system

Years ago Jimmy Weg wrote an awesome blog post on how to create a VMware virtual machine from a raw image file. This is my follow-up on how to virtualize Apple Mac OS X.

Bear in mind that, according to this article in the VMware Knowledge Base: The End User License Agreement (EULA) for Apple Mac OS X legally and explicitly binds the installation and running of the operating system to Apple-labeled computers only.

Having said that, these are the steps to follow.

Prerequisites
  1. WinVMDKCreator (the tool was developed by Dana McNeil and was originally available on Jimmy Weg's blog) 
  2. VMware Workstation (this guide was tested against version 12 Pro)
  3. Patch Tool for VMware (see Install Patch Tool for VMware in the article available here). The two pictures below show the difference before and after installing the patch.
(before)
(after)

Virtualization

#Step 1
Open the raw image with your favorite tool. The following picture shows a Mac mini A1347 I imaged during an investigation. Strangely no encryption was set on that Mac. I haven't tried yet with an encrypted image. I guess you can skip to #Step 3 in that case.


#Step 2
Check which OS X version was installed by looking at the .plist SystemVersion.plist.


In my case the Mac mini was running Mac OS X 10.12 (macOS Sierra).


#Step 3
Launch the WinVMDKCreator tool. Select the image to virtualize under File Data. Tick Set disk image segment file attributes to Read Only. Then press Generate to create the .vmdk file.


#Step 4
Edit with a text editor the .vmdk file just created. Change the value of ddb.virtualHWVersion according to the version used of VMware Workstation.

For instance, if you're using VMware Workstation 12: ddb.virtualHWVersion = "12"

#Step 5
Launch VMware Workstation. From File choose New virtual machine (custom) and set these settings:

Hardware compatiblity Workstation 12.x
Guest Operating System Installation I will install the operating system later
Select a Guest Operating System Apple Mac OS X
Virtual machine name/Location whatever you prefer
Firmware Type EFI (default setting)
Processor Configuration (default settings)
Memory for the Virtual Machine increase to 4096 MB
Network Type Do not use a network connection
SCSI Controller LSI Logic (default setting)
Virtual disk type SATA (default setting)
Select a Disk Use an existing virtual disk
Existing Disk File Click Browse and Open the .vmdk file we previously created with WinVMDKCreator

Click Finish and close VMware Workstation.

#Step 6
Use a text editor to modify the <VirtualMachineName>.vmx file stored in the VM folder.

Append this line at the end of the file:

smc.version = "0"

Without the line above, the VM won't start and will show an error message saying "unrecoverable error: (vcpu-0)".

#Step 7
  • Launch VMware Workstation
  • Take a snapshot of the VM
#Step 8
Now you're ready to fire up the VM!


References

Friday, March 31, 2017

Customizing the filter type in X-Ways Forensics

The Filter:Type in X-Ways Forensics is one of my favorite filters. After many uses, I started thinking on how to make it more suitable for my needs.

This is my tweaked version:


This is a quick summary of the changes:
  • the categories are sorted alphabetically;
  • some categories were renamed;
  • there are now new categories like Network/Packets and Memory;
  • some extensions were moved to other categories;
  • some new extensions/filenames were added to the list.

If you want to give it a try, replace the two files "File Type Categories.txt" and "File Type Categories User.txt" in your installation folder with the ones you can download from my repository xways-forensics .

References

-----------------------------------------------
[UPDATE 03/April/2017]: I added the category Malware, Ransomware which is based on the Ransomware Overview document.
-----------------------------------------------
[UPDATE 11/July/2017]: The custom filter types was added to the Bookmarks menu in the latest version of XWFIM X-Ways Forensics Installation Manager (v1.7.0.0). Thanks Eric!

Saturday, September 5, 2015

Windows Phone 7.8 Forensics

Evidence examination

Mobile device analyzed: NOKIA Lumia 800


The forensic acquisition produced a 15 GB raw image. When I opened the file, all I got was just a list of partitions. None of my tools were able to recognize and parse the file system of each partition. What caught my attention was the size of the last partition (14.7 GB) and the exFAT signature.


Luckily for me, X-Ways Forensics (XWF) is a very flexible tool. My analysis wouldn't have been possible without XWF and the precious help provided by its creator Stefan Fleischmann who improved a lot the parsing of exFAT volumes.

To correctly parse the image with XWF:
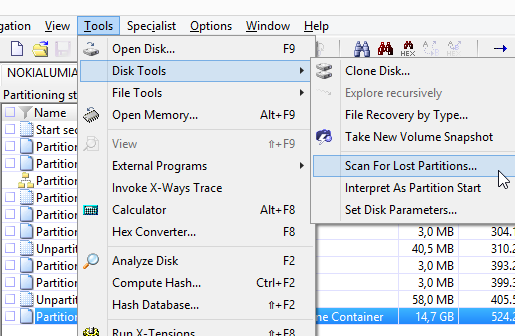
  • open the image with X-Ways Forensics v18.5. From XWF v18.5 beta2, the partition containing Windows Phone data will be shown as WinPhone Container. In the figure below, it's partition 8.

  • Go to Tools | Disk Tools | Scan for Lost Partitions. In the window "Scan For Lost Partitions", tick the first checkbox only and click OK

  • the search will find two more partitions:
  • double click on each of them: one of them will be fully parsed. In my case it was partition 10. Then add the partition to your active case.

The file system is not encrypted. That allowed me to run data carving to recover deleted files, especially pictures and videos.

What follows is a gathering of the main artifacts that I managed to manually extract and parse. Bear in mind that my assumptions could be imprecise or incorrect.

Artifacts

Contacts and Call Log
Contacts are stored in: \Application Data\Microsoft\Outlook\Stores\DeviceStore\store.vol
Call log is stored in: \Application Data\Microsoft\pim.vol

I ran strings against both of the files. I haven't found any timestamp inside the pim.vol file.

SMS messages
Text messages are stored in: \Application Data\Microsoft\Outlook\Stores\DeviceStore\store.vol

In hex view the body of each text message is preceded by the string "IPM.SMS" or "IPM.SMStext". From what I've seen, the timestamp is not nearby the message and I don't know where it could be located. It's possible to distinguish sent messages from received messages by the fact that a sent message lacks the phone number of the recipient in its structure.

Received Message

 
Sent Message

According to what I read in the XDA-Developers forum and on Forensic Focus, Windows Phone periodically creates a XML backup of text messages and stores them in a file named CommsBackup.xml (\Application Data\Microsoft\Outlook\BackupVols). The xml file contains many tags, the most important are:

TAG NAME Description
<Property Name="0x37001f"> body
<Property Name="0x3003001f"> sender/receiver's phone number
<Property Name="0xe070003"> value 21 = sent
value 01 = received
<Property Name="0xe060040"> timestamp (received/sent)

I successfully retrieved thousands of old text messages from unallocated space. In order to carve out deleted SMS XML entries, add the following data to the file File Type Signatures Search.txt located in the XWF installation folder.

Description WP SMS backup
Extensions sms
Header <Property Name="0x1a001f">IPM.SMStext
Offset 0
Footer SMS:ReplaceOption">
Default Size 100/6000

You can manually edit that file with notepad. Just copy and paste at the end of the file:
WP SMS backup sms <Property Name="0x1a001f">IPM.SMStext 0 SMS:ReplaceOption"> 100/6000

Within XWF, press F10, tick the File header signature search checkbox and press OK. In the File header search window, tick the newly created signature and choose complete byte-level search  at the right bottom.

Once finished carving, export all these files to a folder. Use my script wp78_sms_xml.py to automate the parsing of all these carved messages.

Images
Pictures are stored in: \My Documents\Zune\Content\0300\00
The file names are numeric (in hex format) and are in the order in which the pictures were saved on the phone. Even though the phone is running Window Phone 7.8, EXIF metadata shows Windows Phone 7.5. Data carving allowed me to fully recover many deleted pictures.

Bluetooth
The list of received files via bluetooth is stored in:
\Applications\Data\51F49C63-5966-4752-BB12-430455F911A8\Data\IsolatedStore\btsharing.sdf
I used the freeware utility CompactView to open this file and read the table ReceivedFiles.


Emails
Emails are stored in .dat files under:
\Application Data\Microsoft\Outlook\Stores\DeviceStore\data

Downloaded attachments are stored under:
\Application Data\Volatile\EmailAttachments\Attachments[e-mail ID]

The .dat files contain the message body of each e-mail. The header is stored in the store.vol file. A keyword search for the term SMTP in the store.vol file allows to find all the e-mail addresses related to received and sent emails.

In the following picture I show the content of an incoming email that I'd sent to myself from another device during the testing. The email is stored inside a dat file. Its partial header is located inside the store.vol file. I don't know yet how to automate the correlation of these two blocks of information.  


Internet Explorer
Browser artifacts are stored in:

Favorites: \Windows\Favorites <== URL files (both default and personal ones)
Cookies: \Windows\Profiles\guest\Cookies
History: \Windows\Profiles\guest\History\History.IE5\index.dat
Cache: \Windows\Profiles\guest\Temporary Internet Files\Content.IE5

I extracted the entire guest folder and parsed it with full success with Internet Evidence Finder v6.6.

Applications
The two paths \Applications\Data and \Applications\Install contain the same number of subfolders with the same ID names. The data folder contains app settings and user data while install is the installation folder.


In order to retrieve the name corresponding to each ID use the URL:
http://windowsphone.com/s?appid=ID (where ID is the ID you want to search)

Some apps are preinstalled and their IDs are listed here:

I wrote a small python script wp_appid.py that automatically retrieves AppNames from AppIDs.

The app version information is sometimes stored in files named __ApplicationSettings in  \Applications\Data\[App-ID]\Data\IsolatedStore. For instance this one is from the Twitter app:


Wireless Networks
\Windows\Wlan\CommonAppData\Microsoft\Wlansvc\Profiles\Interfaces\{xxxxxxxx-xxxx-xxxx-xxxx-xxxxxxxxxxxx}\{Random-GUID}.xml

Creation time will correspond to the first connection to that SSID.


Adobe PDF Reader
Last opened PDF files are listed in:
\Applications\Data\BC4F319A-9A9A-DF11-A490-00237DE2DB9E\Data\IsolatedStore\ARFileOpenParms.xml

Each entry shows as well when the PDF file was opened.

Copies of opened PDF files are stored in:
\Applications\Data\BC4F319A-9A9A-DF11-A490-00237DE2DB9E\Data\IsolatedStore

WhatsApp (v2.12.72)
The app version information is stored in the file \Applications\Data\218A0EBB-1585-4C7E-A9EC-054CF4569A79\Data\IsolatedStore\version

The phone number in use is located in:
\Applications\Data\218A0EBB-1585-4C7E-A9EC-054CF4569A79\Data\IsolatedStore\settingsv2\nv\settings.db

This file contains the filetime timestamp of when WhatsApp was activated. You can convert it from here: http://www.silisoftware.com/tools/date.php


Messages are stored in a SQLite database:
\Applications\Data\218A0EBB-1585-4C7E-A9EC-054CF4569A79\Data\IsolatedStore\messages.db

Pictures and video shared (received and sent) are stored in:
\Applications\Data\218A0EBB-1585-4C7E-A9EC-054CF4569A79\Data\IsolatedStore\Shared\Transfers\

Received pictures when viewed get automatically saved in:
\My Documents\Zune\Content\0300\00

Deleted messages: I successfully carved out SQLite databases with XWF. That meant thousands of deleted messages recovered.

Twitter (v3.0.1.25063)
The most interesting files are stored in:
\Applications\Data\0B792C7C-14DC-DF11-A844-00237DE2DB9E\Data\IsolatedStore

You can run strings against these files:
{Twitter UserID}.Timeline.dat <== contains tweets that appeared on the user's timeline
{Twitter UserID}.Connect.dat <== notifications for the tweets that got favorited or retweeted
{Twitter UserID}.Friends.dat
{Twitter UserID}.DirectMessages.dat  <== contains direct messages
{Twitter UserID}.SavedSearches.dat <== saved searches on Twitter

OneDrive
Folder:
\Applications\Data\AD543082-80EC-45BB-AA02-FFE7F4182BA8\Data\IsolatedStore\

Under this folder there are files in JSON format with a prefix name ItemViewModel containing metadata of files stored on the user's OneDrive account. These files contain useful pieces of information that inform us if a OneDrive account is in use: DiskQuotaUsage, DisplayQuotaRemaining and DateModifiedOnClient.

In case SyncUpload is active on the phone, we'll also see additional details for uploaded files such as: filename, extension, displaysize, lastaccess, modifieddate, ownername and sharinglevel.

Timestamps are in DateTime format. In the following article, Microsoft explains how DateTime works:
Time values are measured in 100-nanosecond units called ticks, and a particular date is the number of ticks since 12:00 midnight, January 1, 0001 A.D. (C.E.) in the GregorianCalendar calendar.
For instance, 635503790921870000 decodes to 2014-10-31 19:04:52.187000. Here's a post on how to convert from ticks to human readable date.


Registry artifacts

The path \Windows\Registry\ contains two registry hive files: system.hv and user.hv.
Timestamps are encoded in Win64Bit Little Endian.

An old post in the xda-developers forum explains how to convert hv files into text files by using a command line tool named rgucomp. The result is not that good, but it's better than nothing. From the command prompt type:
  • set _FLATRELEASEDIR=.
  • rgucomp -nologo -o system.hv > system.txt
I'll list below some artifacts that can be extracted from the two hives. We can use them as keywords to perform searches in the unallocated space.

Account (user.hv)
The current Microsoft account configured on the phone is located in:

[HKEY_CURRENT_USER\Software\Microsoft\ActiveSync\Partners\{Random-GUID}]
  "LastSyncSuccess"=hex:40,61,20,35,2B,D9,D0,01
  "LastSyncAttempt"=hex:40,61,20,35,2B,D9,D0,01
  "AccountCreateTime"=hex:80,2E,D4,86,FB,D7,D0,01
  "Email"="xxxxxxxxxxx@hotmail.com"
  "User"="xxxxxxxxxxx@hotmail.com"

AccountCreateTime = time when the account was first configured on the phone
LastSyncSuccess = time of last successful sync

Internet Explorer - Typed URLs (user.hv)
URLs typed by the user are located in:

[HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\PreviouslyTyped\[URL]

For example:

[HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\PreviouslyTyped\http://www.ansa.it/]
  "Title"="ANSA.it"
  "Visits"=dword:1
  "LastVisited"=hex:10,2F,A0,FF,FD,D7,D0,01 <== (decodes to August 16, 2015 08:31:50)

IMSI (system.hv)
FriendlyName (device name set by the owner of the phone)
SimImsi (current IMSI)
LastSimImsi (previous IMSI - useful in case we need to know if another SIM card was used)

Bluetooth (system.hv)
name (paired device name - the field "name" is preceded by the keyword "keytype")
LastConnectTime (last connection time to the paired mobile device)

Network address (system.hv)
DhcpIPAddress
DhcpSubnetMask
LeaseObtainedHigh (date and time of when the IP was obtained)
DhcpDefaultGateway
DhcpServer
DhcpDNS

LastShutDownDateTime (system.hv)
LastShutDownDateTime keeps track of the last shutdown time of the device.


GPS coordinates  (system.hv)
  • LastPosInjected (last GPS coordinates injected by an application - e.g. Maps)
  • LastKnownLocation (provides date/time and GPS coordinates - I noticed it got updated when I took geotagged pictures and when I chose Find my phone).
  • LocationSyncStart (time of last location sync)

Download

I wrote three Python scripts to automate the parsing of all the above artifacts. Some pieces of code are taken from the script wp8-callhistory.py written by cheeky4n6monkey.

My following scripts need Python 2.7 and have been tested on Microsoft Windows only:
  • wp78_parser.py: you can run it against specific files or the entire image. Call log and contacts are extracted from store.vol and pim.vol only.
         [UPDATE 03/27/2016]: text message timestamp has been found and decoded
  • wp_appid.py: finds AppNames from AppIDs. If you need to query multiple AppIDs at once, write them in a text file and use the file as input data. When reading from a text file, the script will automatically skip invalid lines and wrong characters. So you don't have to worry about normalizing input data.
  • wp78_sms_xml.py: after carving out SMS xml entries from the forensic image, use this script to do the parsing

You can download the scripts from my Github repository.


Final notes

The following articles have been very helpful to me to understand the structure and location of the data stored on Windows Phone devices: